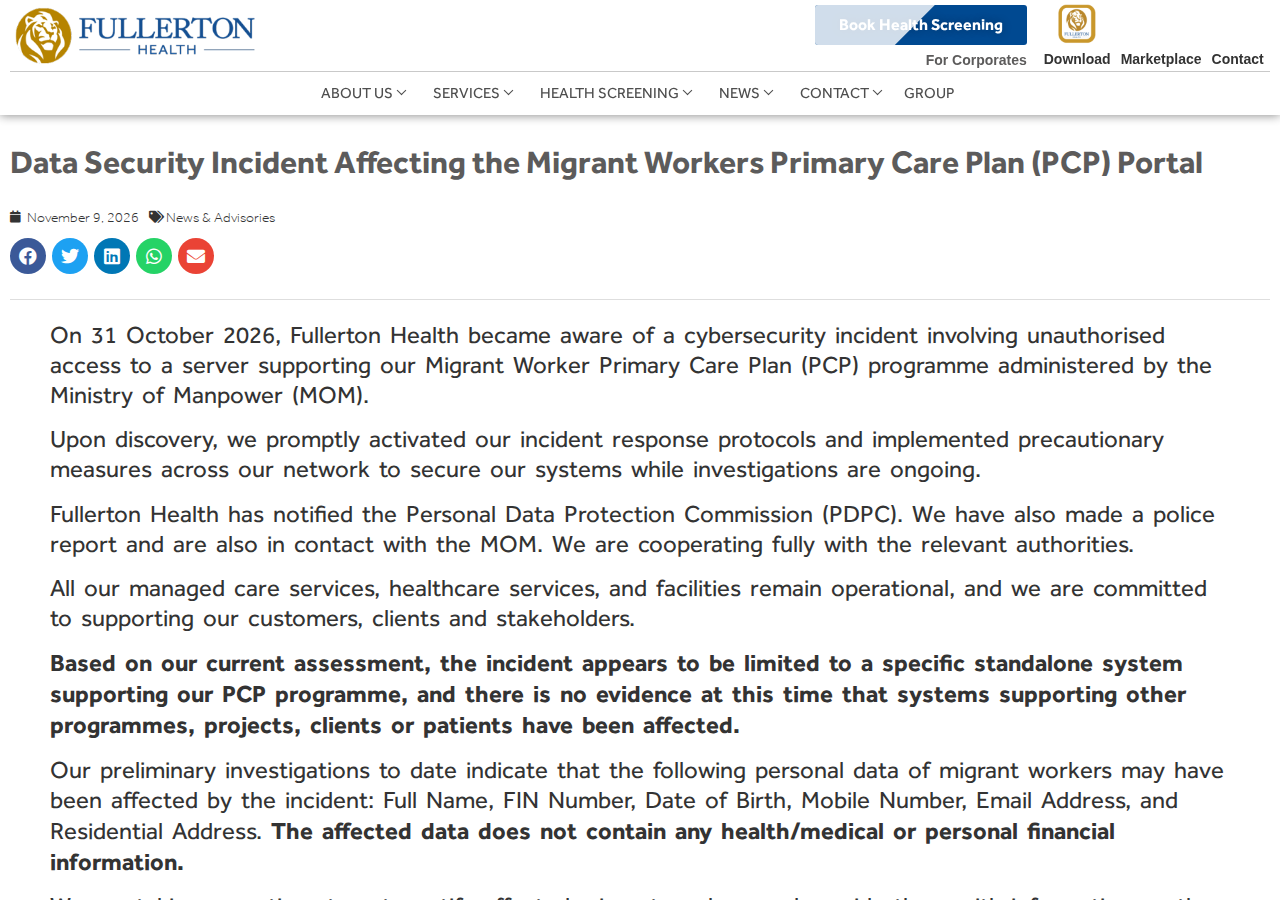
Unauthorised access to a server supporting Fullerton Health's Migrant Worker Primary Care Plan (PCP) programme in Singapore may have exposed the personal data of migrant workers, the healthcare provider confirmed. Discovery came on 31 October 2026, and the notice went up on the company's website on Monday 9 November 2026. Six categories of data may have been affected: full names, Foreign Identification Numbers (FIN), dates of birth, mobile phone numbers, email addresses and residential addresses. The company said no health or medical records and no personal financial information were involved. No victim count was given, so the scale of the incident is still unknown.
Chronology of the incident#
On 31 October 2026, Fullerton Health became aware of the incident and activated its incident response protocols. Precautionary measures were implemented across the company's network to secure its systems while the investigation continued. Nine days passed before the notice appeared on the company's website, on Monday 9 November 2026. CNA, The Straits Times and the Malay Mail reported it the same week.
How the server was accessed has not been disclosed. No attack vector has been reported, no attacker has been named, and no motive has been stated. Neither has the company reported any confirmed external outflow of the data, nor any confirmed misuse of it. The notice says the data "may have been affected". Unauthorised access to the server is confirmed, while exfiltration of a defined set of records is not.
Services stayed up throughout. Fullerton Health said all its managed care services, healthcare services and facilities remained operational. It also said it is cooperating fully with the relevant authorities, and that investigations remain ongoing, with further updates to come as more verified information becomes available.
Data that may have been affected#
Six categories of personal data may have been affected, according to the notice: full names, Foreign Identification Numbers, dates of birth, mobile phone numbers, email addresses and residential addresses. The same six categories appear in the reporting of all three outlets, and the company drew a clear line around what was not involved. The affected data contains no health or medical information, and no personal financial information.
A FIN number is a government-issued identifier for foreign residents in Singapore. It cannot be changed the way a password can. Combined with a full name, date of birth, mobile number, email address and home address, it gives an attacker enough material to build a convincing identity for phishing and fraud attempts. No single field opens an account on its own. Together, the fields let an attacker impersonate a worker to a bank, an employer, a government service or the worker themselves. A leaked address becomes the starting point for that kind of attack, because password resets and official notices flow through the inbox, as How an email address leads to identity theft explains.
The email address carries a second risk. An attacker reaches the worker through that address, and the worker's own accounts use it for recovery too. A phishing email sent to an address the worker gave to a healthcare programme, naming the worker and referencing the PCP programme, is far more convincing than a generic scam message. The pattern is described in How phishing uses a leaked email: the leaked details supply the personalisation, and the personalisation supplies the trust.
Migrant Worker Primary Care Plan#
Eligible migrant workers in Singapore receive affordable primary healthcare through the PCP programme. The Ministry of Manpower (MOM) administers it, and employers must buy PCP coverage for certain work permit and S Pass holders, including workers in the construction, marine shipyard and process sectors. Because that coverage is mandatory, the affected population could be large even though no victim count has been given. The programme covers a defined and sizeable workforce, and the server held the personal details of workers enrolled through it.
Some of the people affected may need more help understanding how they have been affected and what precautionary steps they can take. The company acknowledged this. Guidance will form part of the notification process, the company said. It is taking steps to notify affected migrant workers, tell them about the incident, and point them to where they can seek further assistance. Some of those affected may face language barriers, limited familiarity with Singapore's data protection process, and dependence on employers for information about a programme their employer bought on their behalf.
Company response and regulatory action#
The Personal Data Protection Commission was notified, a police report was lodged, and the Ministry of Manpower was contacted. CNA received confirmation from the PDPC that it is aware of the incident and is investigating, and a PDPC spokesperson confirmed the same to The Straits Times. The company said it is giving the relevant authorities its full cooperation.
The incident also appears limited to a specific standalone system supporting the PCP programme, the company said. That is the company's own assessment, qualified in the notice itself with the words "appears" and "at this time". According to the company, there is no evidence at this time that systems supporting other programmes, projects, clients or patients have been affected. What the ongoing investigation finds will decide whether that assessment holds. Further updates will follow from the company as more verified information becomes available.
In its statement, Fullerton Health said: "Protecting personal information is one of Fullerton Health's highest priorities and we deeply value the trust that our stakeholders have placed in us. We sincerely regret any concern or uncertainty this incident may have caused."
Precautionary measures for affected workers#
Affected migrant workers are being notified directly by Fullerton Health, with guidance on precautionary measures included in that notification. A notification's guidance should be read first by any worker who receives one, because it will reflect what the company knows about which records were on the affected server.
The standard steps for a breach of this kind are straightforward, beyond the company guidance. Any email, text message or call that references the PCP programme, a FIN number or Fullerton Health details should be treated with caution. It should be verified through a channel the worker already trusts, rather than through a link or number in the message itself. The signs to look for are covered in How to check if an email is phishing: a sender address that does not match the organisation it claims to be from, pressure to act quickly, and requests for passwords or payment details.
A check of whether their email address appears in a known breach is also worth doing. That check is run by Have I Been Pwned, which explains what each result means. The incident has not been reported as listed in Have I Been Pwned yet, so a clean result would not prove an address was unaffected, because listing depends on the data being verified and loaded. A reused password should be changed on each account, starting with email, for workers who reuse the same password across accounts. A leaked email address combined with a reused password is the combination that opens accounts. Those steps are walked through in order in What to do when your email is in a data breach.
Your address is probably in this file. Check whether it is, do the password work above, and then fix the part you control: the address you hand out next time. One AliasFleet alias per service means the next leak can only point back to the service that leaked it. Founders Club is $7 a month, locked forever, instead of $12. Early members only.
Related Singapore disclosures#
Several other Singapore breaches were reported in the same fortnight, and the Fullerton Health incident follows them. Telco M1 disclosed a breach on 30 October 2026. Telehealth provider Doctor Anywhere reported a leak of users' personal data, with clinical records not affected according to forensic specialists. Singapore Airlines said data relating to booking records was accessed in a breach involving software provider Amadeus. SPH Media said its systems were hit by cyberattacks, and food solutions provider SATS disclosed that Tappee, a school meal ordering application, had been affected by a cyber incident.
No reported evidence links these incidents to each other. Two of those incidents have coverage on this blog: the M1 data breach and the SPH Media data breach. The Amadeus incident behind the Singapore Airlines disclosure is covered in the Amadeus airlines data breach article.
State of the investigation#
The investigation is ongoing, and the facts that would settle the scale of the incident have not been disclosed. How many workers were affected, how the server was accessed, whether the data left the company's systems, and whether any of the data has been misused: none of this has been stated by the company. More detail may come from the PDPC investigation, and further updates will follow from the company as more verified information becomes available. Until then, what is verified is the discovery date, the notice date, the six categories of data that may have been affected, the absence of health and financial data, and the regulatory notifications the company has made. A victim count is the next update worth watching for. It would turn an incident of unknown scale into a measured one. Any statement from the Ministry of Manpower is also awaited. The ministry administers the programme and has been contacted by both CNA and The Straits Times for more information.
