
Double Counter disclosed on October 5 that attackers broke into its systems on October 4 and copied about 12 GB from one of its databases, including around 1 million email addresses. I run AliasFleet: one email alias per account, so a leaked address names the company that lost it. The million addresses are the headline. The part that bothers me is the other file: about 28 million Discord usernames and IDs swept up as a byproduct of server verification, from people who never signed up for anything.
The attack, in the company's own words#
Double Counter published a detailed incident report, INC-2026-10-04, the day after the attack. The facts, from the company:
| What happened | Detail |
|---|---|
| Attack window | October 4, 2026, 12:03 to 17:54 UTC; service restored 19:19 UTC |
| Entry point | A retired server from the old hosting setup, still publicly reachable, running a self-hosted Metabase analytics tool |
| Method | A vulnerability in Metabase let the attacker forge an administrator session, then use cloud credentials stored on that server |
| Data copied | About 12 GB from one database (15:09 to 15:34) |
| Bot abuse | The stolen bot token posted the attacker's server links in about 50 large Discord servers |
| Payment fraud | A stolen Stripe key was used for $7,316 in test charges on a company card and $3 and $15 on two customers' cards; all refunded |
"The entry point was an old server from our previous OVH hosting setup. It was no longer in use and no longer linked to the operational Double Counter service." (Double Counter incident report, October 5)
The attacker probed that forgotten server from rotating VPN addresses starting October 3, worked through a list of usernames, and was in by 00:47 on October 4. From there they used two legitimate credentials found on the box, a service-account key and a saved admin session, and spent the afternoon inside Double Counter's cloud. No new accounts were created, which is partly why the activity blended in. The company says a full audit of its cloud projects found no backdoor left behind, and the service was restored at 19:19 with new credentials.
What was copied#
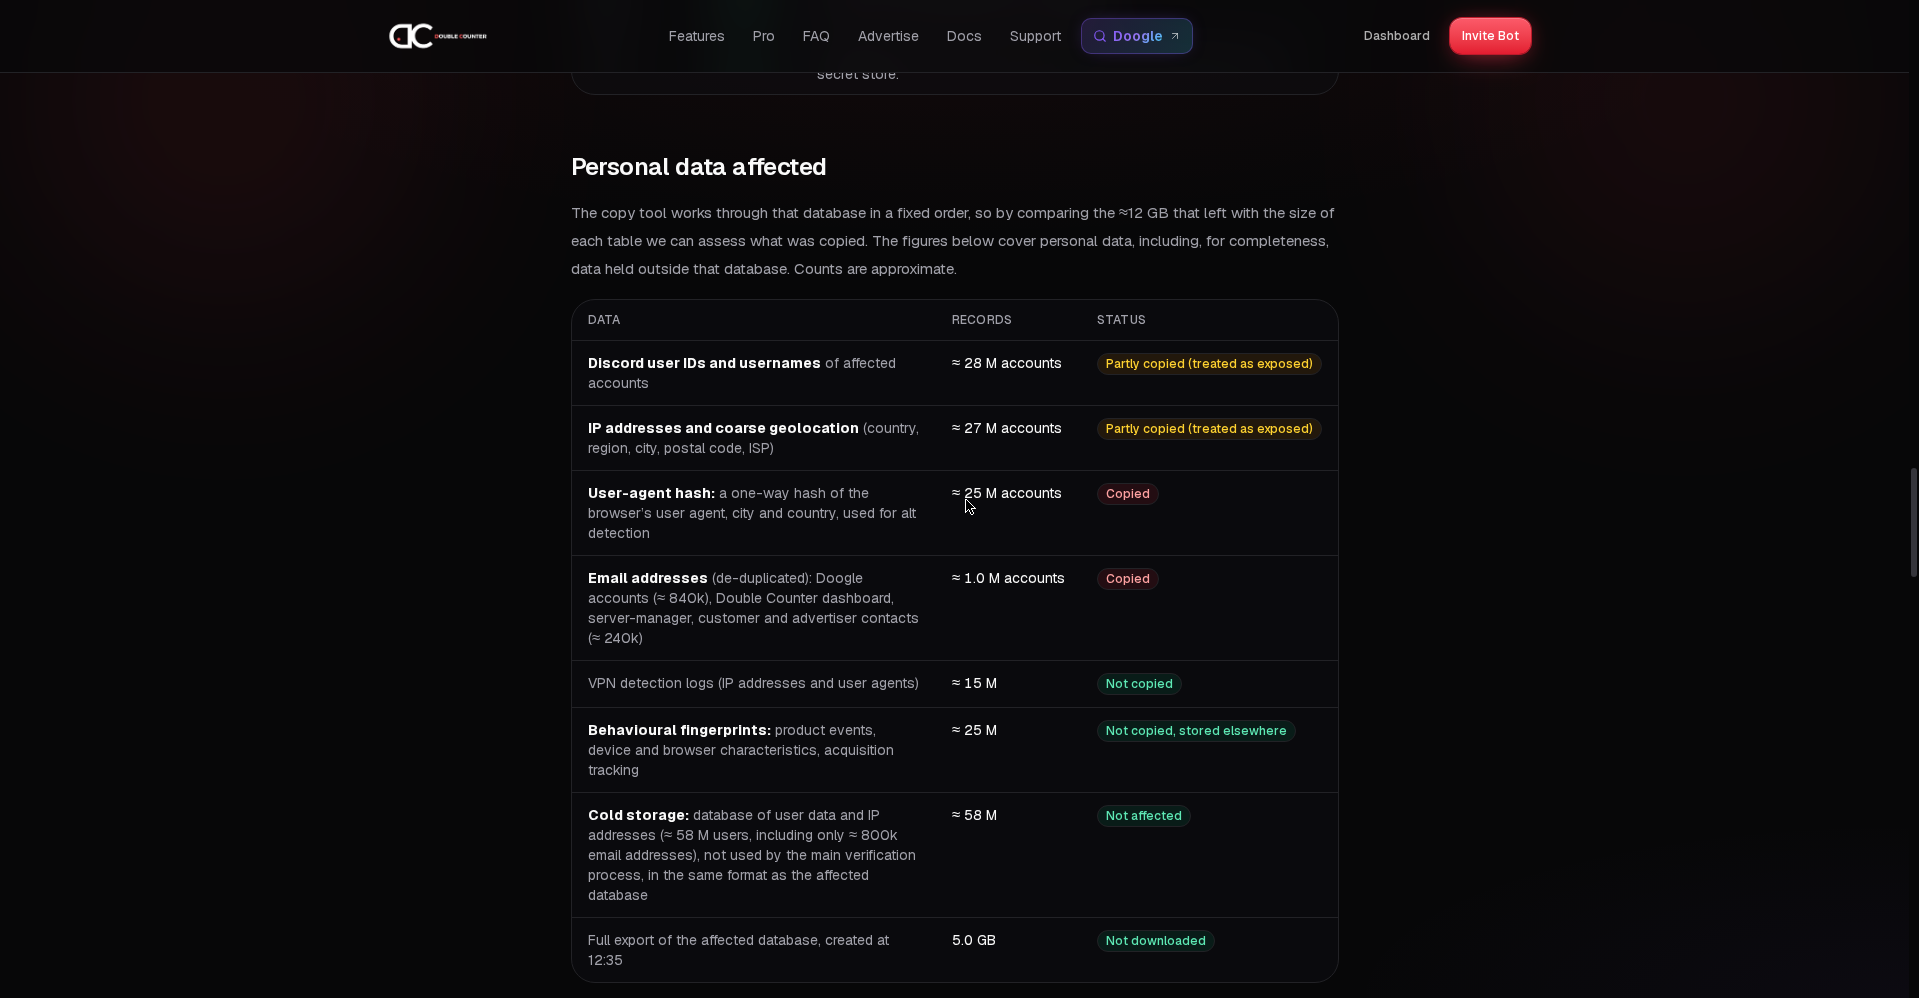
The company's data table, treated as exposed where the copy was partial:
| Data | Records | Status |
|---|---|---|
| Discord user IDs and usernames | About 28 million | Partly copied, treated as exposed |
| IP addresses and coarse geolocation | About 27 million | Partly copied, treated as exposed |
| User-agent hashes for alt detection | About 25 million | Copied |
| Email addresses (de-duplicated) | About 1.0 million | Copied |
| VPN detection logs | About 15 million | Not copied |
| Behavioural fingerprints | About 25 million | Not copied, stored elsewhere |
| Cold storage database | About 58 million users | Not affected |
The email figure splits into about 840,000 Doogle accounts and about 240,000 Double Counter dashboard, server-manager, customer, and advertiser contacts. Have I Been Pwned added the breach on October 7 and lists 274,922 unique email addresses with Discord usernames as published publicly. That is the subset circulating in the open; the company's copied set is the full million.
Not affected, per the company: the cold-storage database, the behavioural database, Discord passwords (which Double Counter never receives), and stored card details (held by the payment provider).
The server nobody decommissioned#
The detail I keep coming back to is the retired server. It was not part of the live service. Nobody used it. It just sat there, publicly reachable, running an analytics tool with a known-flaw-shaped hole in it, holding live cloud credentials in its saved sessions. The attacker did not defeat Double Counter's current infrastructure. They walked through a door the company had forgotten it owned.
There is a pattern forming around Metabase specifically. In August 2026, a Metabase zero-day (CVE-2026-72898, CVSS 10.0, on CISA's exploited list) was used against Framework and Tally, both of which disclosed customer data exposure. The Register's reporting on the Framework breach and the TechTimes writeup describe attackers pivoting from the analytics tool into everything it could reach.
What I will not claim is that this was the same flaw. Its report describes a vulnerability that let the attacker forge an administrator session in a self-hosted instance, and names no CVE. It could be the August zero-day on an unpatched box, or something else entirely. Treat the Metabase link as a pattern, not a confirmed cause.
The trusted bot is the phishing kit#
The second half of the attack deserves as much attention as the database. With the stolen bot token, the attacker posted invitations to their own Discord server in about 50 large servers that use Double Counter. Those messages appeared as sent by Double Counter itself.
This is the same trick I wrote about in the Nikkei breach: when the message comes from a trusted account, the usual checks collapse. Nobody scrutinises a message from the verification bot their server already trusts. Double Counter's own advice to server administrators is to delete any such message sent on October 4 between 12:00 and 16:30 UTC and to check the audit log for the bot's actions in that window.
Now pair that with the stolen data. The file ties Discord usernames to email addresses and IP-based locations for a large slice of victims. That is a ready-made kit for Discord-targeted scams: fake re-verification DMs, "your account needs confirming" messages, Nitro giveaways aimed at exactly the right usernames. The attacker already proved they will use the trusted channel. Expect them to use the trusted data next.
Double Counter's bot was used to advertise the attacker's server. Treat any surprise invitation, re-verification request, or "security check" DM referencing Double Counter as hostile. Get to your server's settings through the Discord app yourself; never follow the link in the message.
If you are in the file#
Work from the assumption that you are, if you ever verified in a Discord server running Double Counter, held a Doogle account, or touched its dashboard. Here is what to do.
- Check Have I Been Pwned now. The breach is listed, and the published subset is already there. Turn on notifications while you are at it.
- Expect Discord-flavoured phishing. The stolen set pairs usernames with emails and rough locations, which is everything a scammer needs to write a message that feels personal. Fake verification requests and Nitro scams are the obvious plays.
- Server admins: follow the company's instructions. Delete the October 4 messages, check the audit log for Double Counter's actions between 12:00 and 16:30 UTC, and tell your members what happened.
- Turn on multifactor authentication on your email account. Your email is the recovery path for everything else, and it is the one field confirmed copied for a million people. A passkey is best.
- Watch for breach-notification impersonation. The disclosure is public, so fake "Double Counter security update" emails are coming. Real updates live on the company's own site, not in your inbox.
The breach-response guide walks through all of this in order.
What one alias per service buys you here#
Here is the structural problem this breach puts on display. Millions of the people in that 28-million file never created a Double Counter account. They clicked verify in a Discord server, and the bot logged their username, their IP, and in a million cases an email address. "Be careful who you give your email to" does not work when nobody gave it. The collection happens as a side effect of joining a community.
A per-service alias does not stop the collection, but it changes what the leak costs you. If the address you gave Doogle or the Double Counter dashboard existed only for that service, the moment Have I Been Pwned flags it, the alias names the source with no investigation. Every email landing on it from now on has exactly two possible senders: the company, or whoever took the file. Pause the alias and the whole phishing channel dies while your real inbox stays untouched.
That is the leak-tracing mechanism doing its job. Verification bots, game launchers, event signups, any service that collects your address as a byproduct rather than the point: those are the places a unique alias pays for itself. If you have not used one before, this is what an email alias is, and the set-up guide takes about two minutes.
What is still unclear#
The company named no attacker and no CVE, so the Metabase connection stays a pattern rather than a confirmed cause. There is no word on regulatory reporting. The report does not say where the 274,922-record corpus was published or who else holds the full million. And the partially copied tables are treated as fully exposed because the company cannot tell which rows left, which means the true victim count sits somewhere between the published subset and the assessed totals. Watch the company's own report page for updates, not your inbox.
